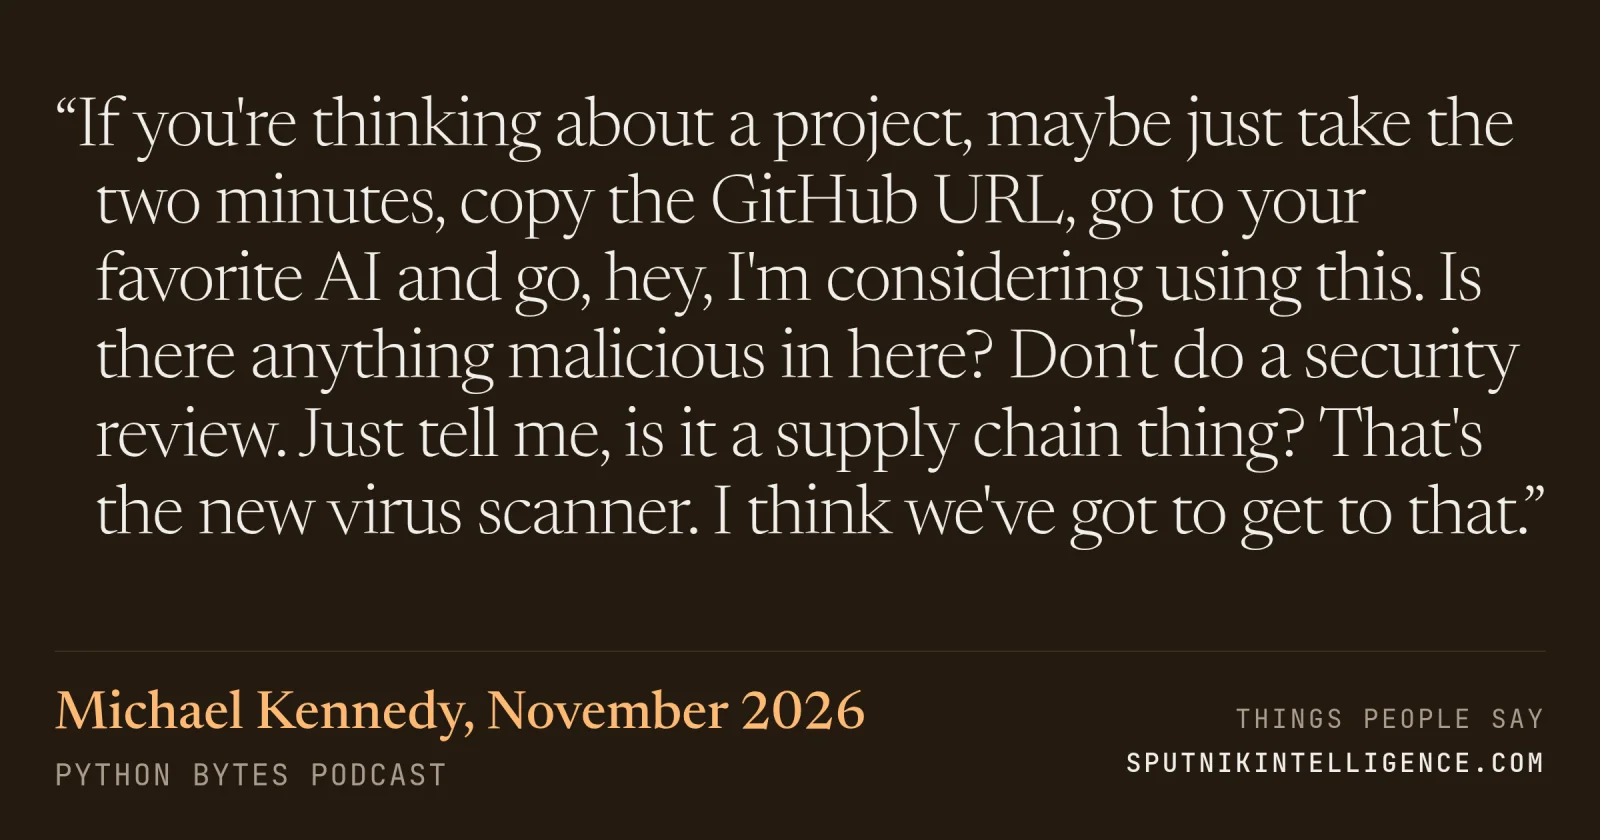
After a segment on honeypots and supply-chain attacks, Michael Kennedy suggests asking an AI model to vet any unfamiliar repository before using it. It's his advice, not a tested method.
I mean, not cool that it's happening, but I love the idea of honeypots and these canaries and type of things. They're really great.
Especially if it's your hobby and you want to see what's going on and experience it. If you can get one of them hitting your honeypot, then you'll gather data from the attackers.
Yeah, absolutely. Now, before we move on to my extra, we were talking before the show, but it feels like maybe worth bringing it out to the audience now. As I go around and look at these different projects that people send me and so on, you never know what's out on the internet, right? There's all the supply chain stuff. So if you're thinking about a project, maybe just take the two minutes, copy the GitHub URL, go to your favorite AI and go, hey, I'm considering using this. Is there anything malicious in here? Don't do a security review. Just tell me, is it a supply chain thing? And just, you know, that's the new virus scanner. I think we got to get to.
These repositories have hooks potentially in them that could run code on your machines. And you clone it. And then if you change into another branch, there's a hook that can fire that can do whatever it wants.
Isn't that nice? I get an extra little bit of execution that I didn't expect. It was convenient.
It was convenient as developers because we would use it for certain things, but it's also very convenient for attackers.