 CJ Reynolds
Senior creator at Syntax and host of Coding Garden, covering web development, JavaScript tooling and AI coding tools.
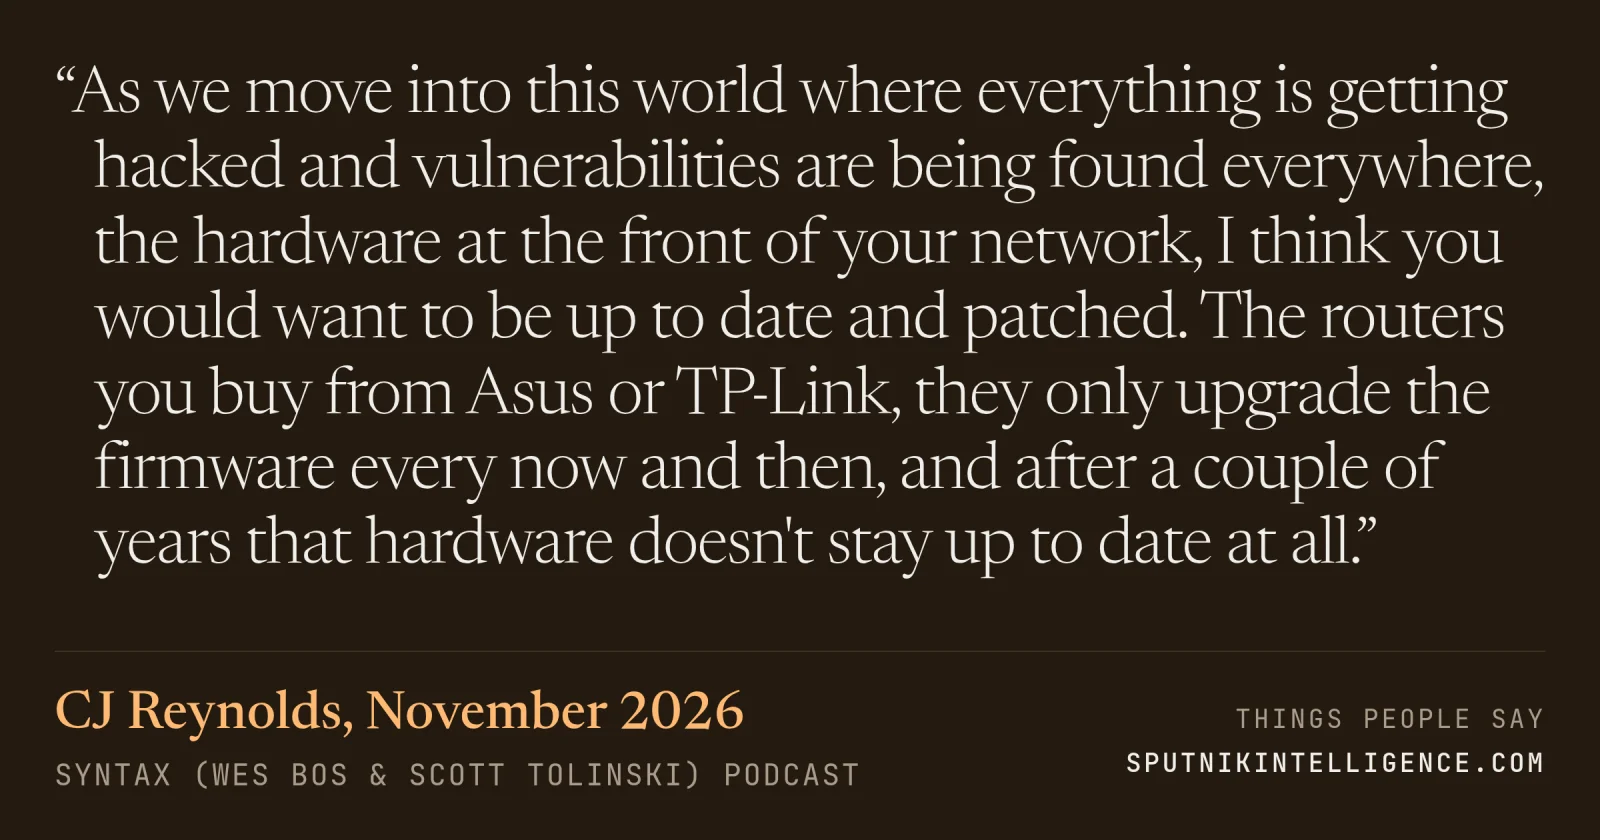
“As we move into this world where everything is getting hacked and vulnerabilities are being found everywhere, the hardware at the front of your network, I think you would want to be up to date and patched. The routers you buy from Asus or TP-Link, they only upgrade the firmware every now and then, and after a couple of years that hardware doesn't stay up to date at all.”
Syntax (Wes Bos & Scott Tolinski) · Hands-On Engineering Podcasts · November 2026
Context
Explaining why he runs his own firewall box instead of a consumer router, Reynolds says patching is the reason: consumer routers are effectively abandoned after a couple of years.
Transcript
Gotcha. Cool. Should we talk about network?
Let's talk about network.
Okay. So I built a completely custom, not built, I didn't build it, but I bought a bare bones machine that's built for being a dedicated hardware firewall. But this machine has four 2.5 gigabit Ethernet ports and then two SFP plus ports plus like USB and everything else. But the idea is you can run a dedicated firewall operating system on it. And this acts as your router and firewall. So most people I would say that haven't looked into this probably just use the router that's given to them by their ISP or the modem and then use maybe they plug a router into that. I started looking into this a lot and one of the issues with the like even the routers that you buy from Azus or TP-Link or some of these other companies, they only upgrade the firmware every now and then, right? Like they, and then after a couple of years, that hardware like isn't, doesn't stay up to date at all. And so as we move into this world where everything is getting hacked and vulnerabilities are being found everywhere, like you, the, the hardware at the front of your network, I think you would want to be up to date and patched. And so that's why I put this machine together. And this…
oh, classic drama. Yeah,
so, but a lot of people use OpenSense. And this is based on FreeBSD, but it basically gives you a web dashboard where you can manage all of your firewall rules. You can set up and explicitly say for each one of those Ethernet ports, what do they do? Should they be receiving internet or sending…
be connected. Yes. You got to be. That's my job.
More from Syntax (Wes Bos & Scott Tolinski)