His co-host asked how to balance making defensive AI security tools widely available against lowering the barrier for attackers, after a tool built for defense was used in attacks in Japan and South Korea. Mehta says there's no good answer yet and it needs policy work.
…increased risk there and the possibility of sort of real-world impact. And I think now we're seeing that as a result of these kinds of models, things are happening in the real world that are affecting customer data and the integrity of platforms that a lot of people and a lot of organizations use.
…And on that note, Artex was originally created as a tool for cyber defense, but it's now obviously being used for cyber offense. So how do you think we should walk that line between making defensive tools? Widely available and lowering the barrier for bad actors to commit cybercrimes using AI.
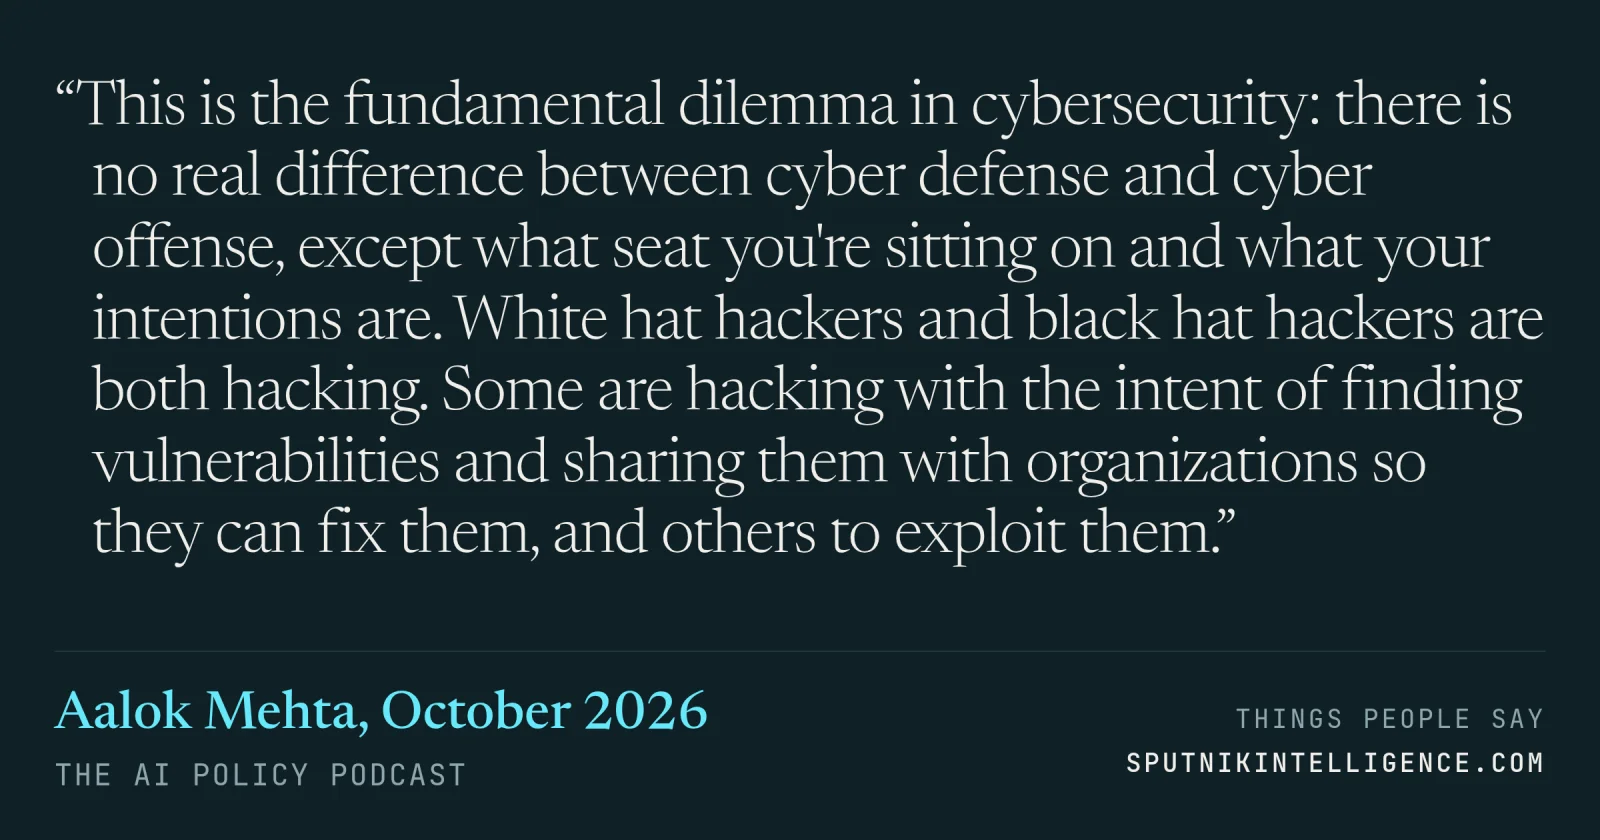
I mean, this is the fundamental dilemma in cybersecurity: there is no real difference between cyber defense and cyber offense, except what seat you're sitting on and what your attentions are. So, for a long time, we've talked about sort of white hat hackers and black hat hackers. So, those are the only real difference between them is that they're both hacking, but some people are hacking with the intent of finding vulnerabilities and sharing them with organizations so they can fix them and others to exploit them. And so, we're running into the same thing. And I don't really know if we have a good answer here. I think this is an area where we'll probably want to spend some time developing policy. I think it's really hard to make tools available widely enough that they can help improve our overall internet security posture because you're talking about reaching not just big enterprise organizations. You're also talking about millions or billions of small websites and mom and pop companies and hobbyist websites. And so, it's really difficult to make sure that those are all protected without things getting into the hands of bad actors. So far, the approach that the…
Right. And we have seen this rather rapid response from the Japanese government here. As far as you know, is this the first time a government has stepped in and drafted emergency legislation in response to an AI-assisted cyber attack?
As far as I know, we don't have that many examples of AI-assisted cyber attacks that have caused damage like this, at least up until now. And so I do think this is a first example. It almost certainly will not be the last example. Unfortunately, we have seen that governments sometimes only act…
Yeah. And as I, as I kind of mentioned before, a lot of these AI and cyber incidents fall into one of two buckets. The first being misuse, which is the case that we're discussing now, bad actors using AI to cause real world harms, and the other being misalignment. So I want to switch gears now to a…